Evidence for your auditors, drawn from the work itself
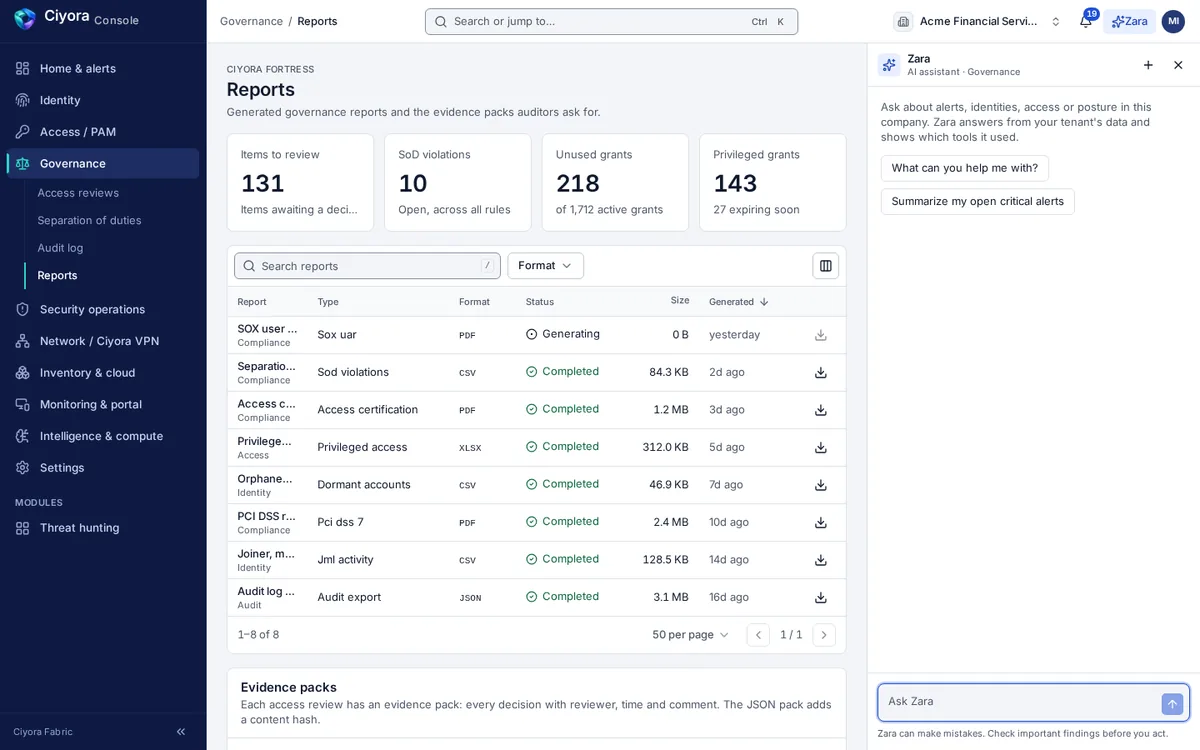
Ciyora Comply connects what the other modules already do (access reviews, separation-of-duties checks, privileged sessions, posture findings and the audit chain) to the controls in the frameworks you report against. Evidence comes from the platform's own records instead of screenshots collected by hand.
What Ciyora Comply does
A framework library with an India regulatory pack
Comply keeps a library of frameworks and controls, including the RBI IT governance directions, SEBI CSCRF, CERT-In directions, IRDAI cyber security guidelines and the DPDP Act, alongside ISO/IEC 27001, SOC 2, PCI DSS and NIST. Equivalent controls are mapped across frameworks, so one piece of evidence can support several of them.
Access review evidence packs
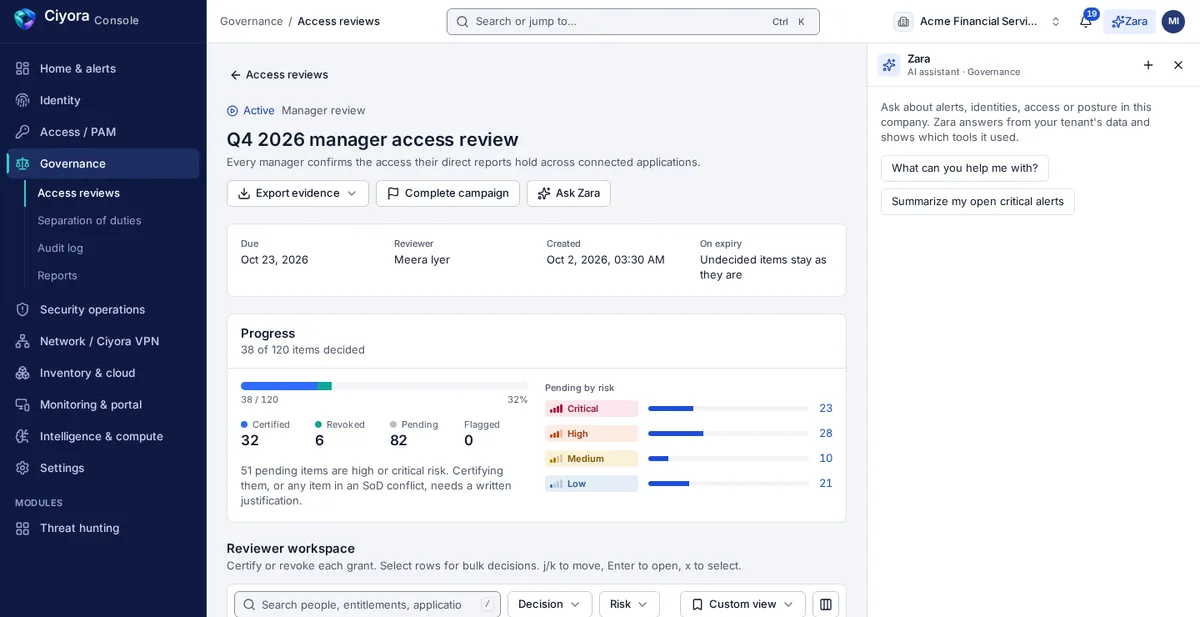
Every access review campaign produces an evidence pack: each decision with reviewer, time and comment. The JSON pack adds a content hash so the file can be checked later.
An audit trail that proves itself
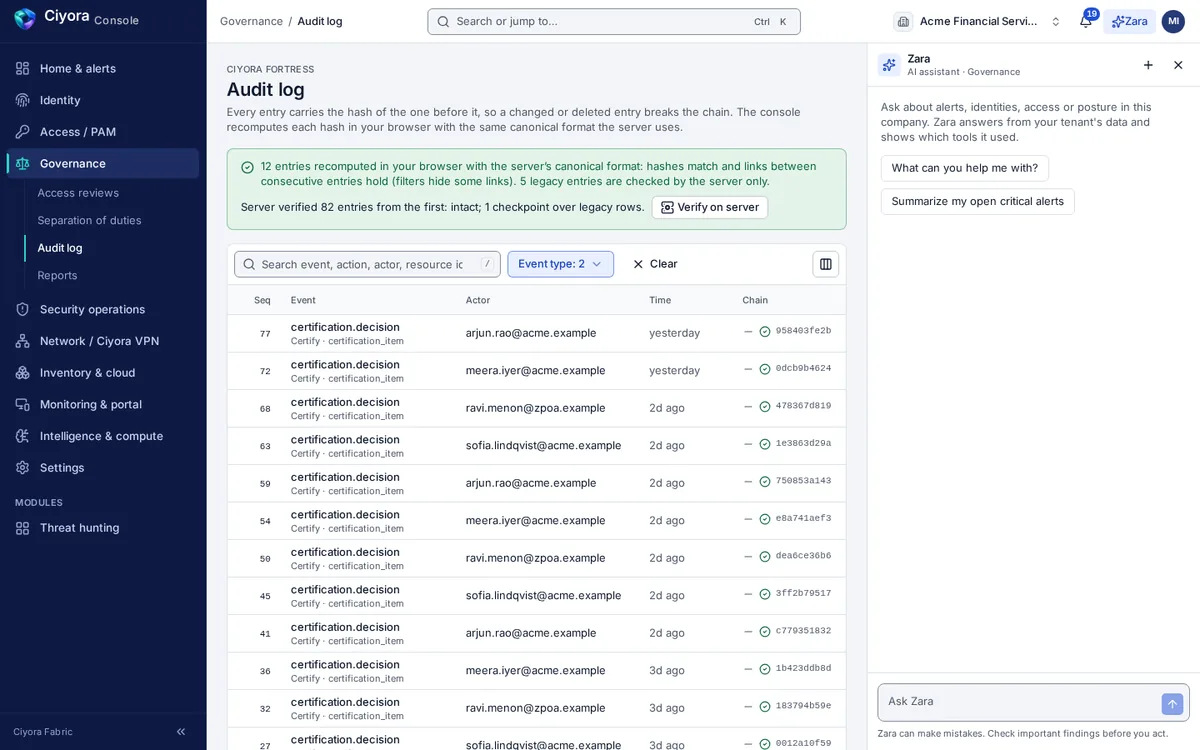
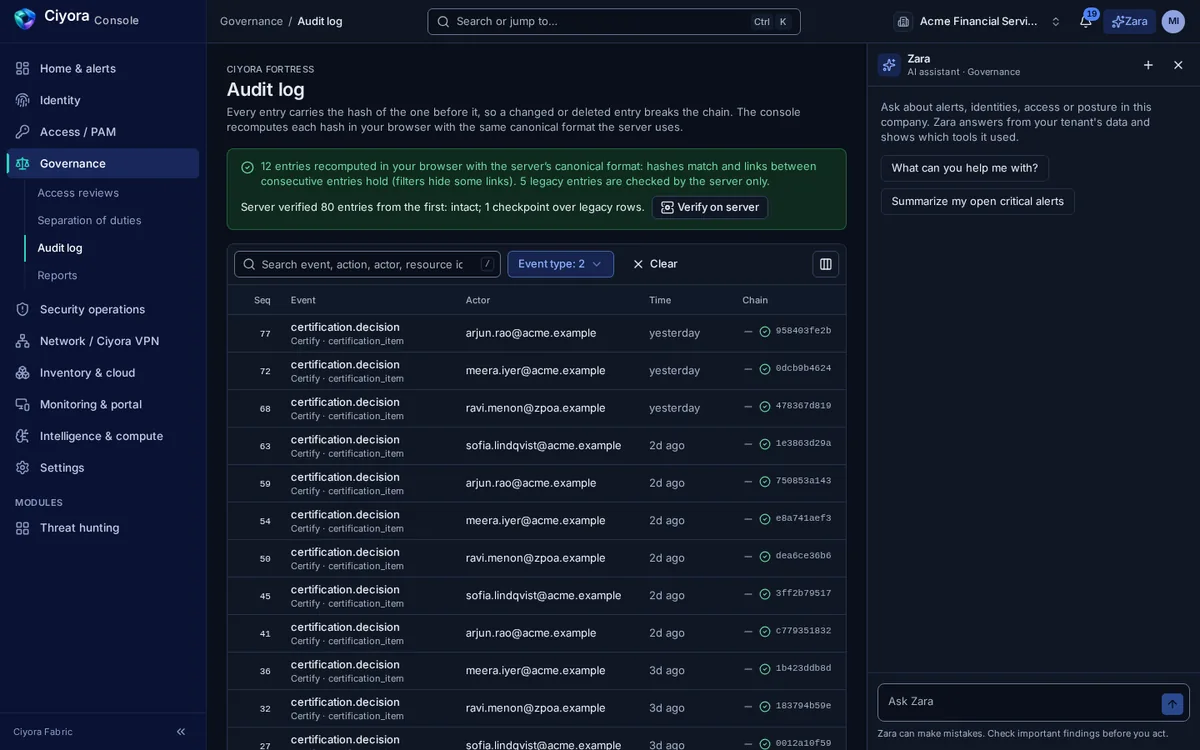
Each audit entry carries the hash of the one before it. The console recomputes the chain in your browser and can ask the server to verify it from the first entry, so a changed or deleted record is detectable.
What Comply does not do. No tool can make an organization compliant or certified. Comply helps you operate controls and show evidence of them; your auditors and regulators decide whether you meet a requirement. See how this works for RBI, SEBI CSCRF, the DPDP Act and ISO/IEC 27001.
Capabilities
- Frameworks and controls
- Framework library, control equivalence across frameworks, and an India regulatory pack.
- Evidence
- Access review evidence packs, separation-of-duties results, privileged session records, posture findings mapped to controls, and audit exports.
- Reports
- User access, SoD violations, access certification, privileged access, dormant accounts, joiner-mover-leaver activity and audit exports in PDF, CSV, XLSX or JSON.
- Audit chain
- Per-tenant SHA-256 hash chain over canonical entries, verifiable in the browser and on the server.
How Ciyora Comply works with the rest of the platform
Every module shares one tenant, one identity model, one audit chain and one console, so a finding in one place is context everywhere else.
Ciyora Comply can be bought on its own or as part of a bundle. See Ciyora Comply pricing.
See Ciyora Comply in a demo
A demo walks through the module on a sample tenant and covers how it would connect to your identity provider, cloud accounts and sites.