The platform under every Ciyora module
Ciyora Fabric is the shared foundation: one control plane, one mesh, one data pipeline, one tenant model and one audit chain. Every module runs on it, which is why adding a module does not add another agent, another console or another set of firewall rules.
How the pieces fit
Everything you run on your side connects outward. Everything that holds state runs in Ciyora Fabric, scoped to your tenant.
Your environment
Ciyora Fabric
Single sign-on through your identity provider. Every API call carries the tenant it acts on.
Cloud and SaaS
Decisions made once, inherited by every module
Gateways and clients dial out
Site gateways register with Ciyora Fabric over an outbound connection using a gateway enrolment key, then learn their peers from the network map the control plane streams to them. Collectors forward events outbound over HTTPS and buffer to disk if the link drops. Nothing in your network has to accept an inbound connection from the internet.
A mesh, with relays only when needed
Ciyora Client and gateways build WireGuard tunnels directly to each other, traversing NAT where possible. When a direct path is blocked, traffic is carried by an encrypted relay. The control plane hands out keys and policy and is not in the data path for direct connections.
Tenant isolation
Each customer is a tenant. People sign in through your identity provider, and the organization in their token selects the tenant. Every API request carries the active tenant, which is checked against the token, and every query is scoped to it. Sensitive values such as vault secrets and connector credentials are encrypted with a data key unique to the tenant.
A hash-chained audit log
Audit entries are written to a per-tenant chain: each entry includes a SHA-256 hash of the previous one over a canonical form, appends are serialised, and updates and deletes are blocked in the database. The console can recompute the chain in your browser and ask the server to verify it from the first entry.
India hosting
Hosted in India · data stays in India. Data processing follows DPDP Act 2023 obligations. Organizations that must keep the platform inside their own boundary can discuss a self-hosted deployment with us.
Built in Go
The API, workers, gateway, relay and Ciyora Client are written in Go and ship as single binaries. That keeps gateways light enough for a small VM and makes self-hosted operation straightforward.
Hosted in India, or run it yourself
- Ciyora-hosted
- We operate Ciyora Fabric. Hosted in India · data stays in India. Data processing follows DPDP Act 2023 obligations. You deploy gateways, collectors, the endpoint agent and Ciyora Client; they connect outbound to your tenant.
- Self-hosted
- For organizations that need the platform inside their own boundary, Ciyora Fabric runs on Kubernetes under a signed licence that sets plan, seats and expiry. Ciyora Client can be pointed at a self-hosted control plane.
- Gateways and clients
- Gateways run on a Linux VM or as a container in each site or VPC. Ciyora Client and the endpoint agent install on Windows, macOS and Linux, with enrolment tokens you control.
Where people meet the platform
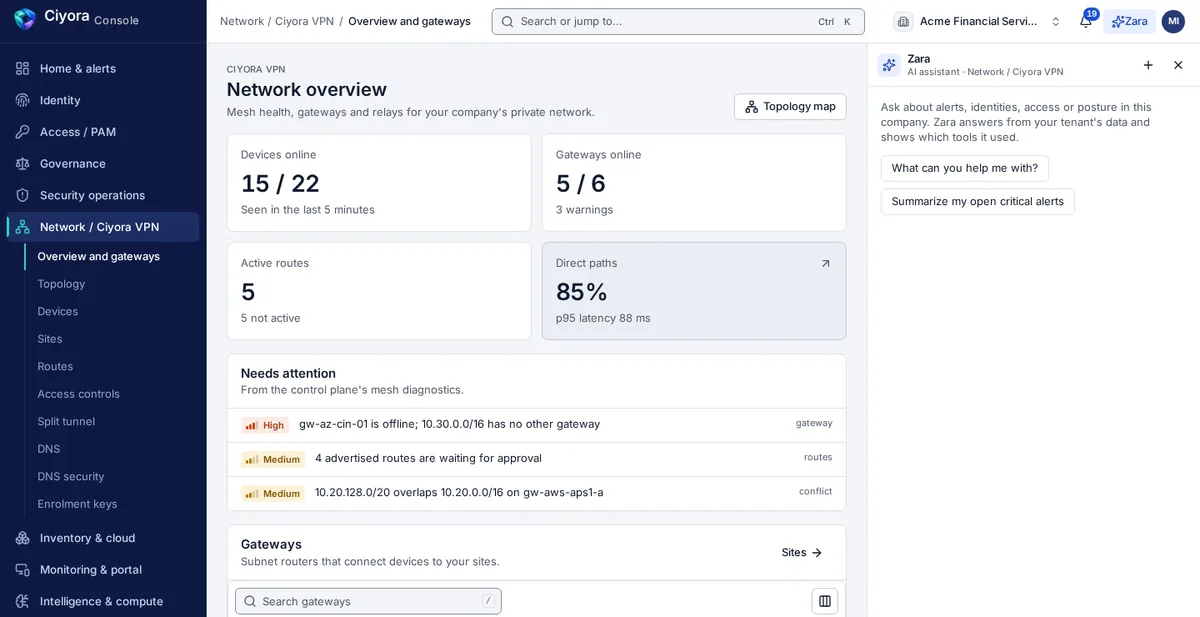
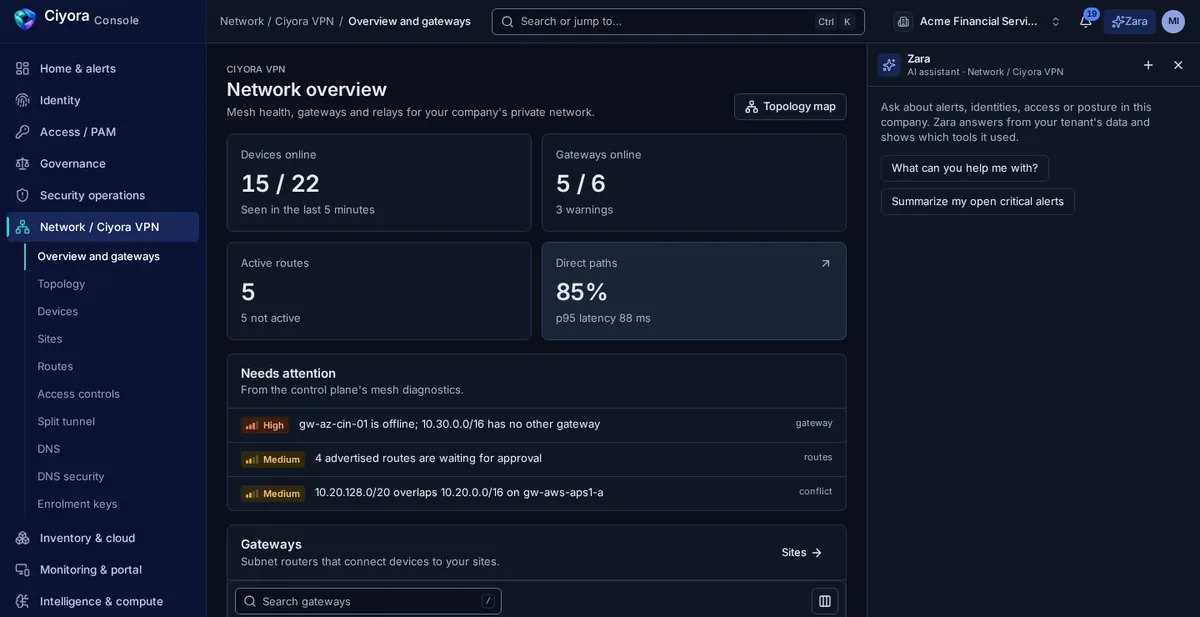
Ciyora Console
The web console for every role, from administrators and SOC analysts to approvers and employees.
About Ciyora ConsoleCiyora Client
The endpoint client for mesh access, split DNS and device posture on Windows, macOS and Linux.
About Ciyora ClientIntegrations
Connectors for identity providers, HR systems, cloud accounts, ITSM, SIEM and security tools.
See integrationsBring your security architects
We are happy to walk through the architecture, the data flows and the deployment model with your review team.